An advanced, innovative solution for the comprehensive protection of hybrid cloud infrastructure. It supports secure development for software systems that use containerized virtualization
PT Container Security
What is container security?
Container technologies such as Docker and Kubernetes are the backbone of modern DevOps processes. Container security involves the protection of containers, the infrastructure in which they run, and the applications that run in these containers during build, deployment, and execution. It's also important to protect containers at the cluster and orchestrator level.
Protecting containers is challenging because traditional cybersecurity tools are often incompatible with containerized environments. However, with the advent of DevSecOps, organizations have become aware of the importance of integrating container security throughout the entire development lifecycle. Container security must comply with the organization's policies and processes.
Why is container security important?
Omnipresent use of container technology, rapid digital transformation, increasing complexity and sophistication of cyberthreats, and extensive research and development (R&D) are pushing companies to implement cybersecurity tools for containerized environments.
Positive Technologies developed PT Container Security to address the needs of Russian companies to improve the efficiency of software development processes, boost digital transformation, and strengthen information security. This product is designed to protect the IT infrastructures of companies that use containerized virtualization. It provides a set of security tools for various stages of the software lifecycle and grants access to actionable cybersecurity insights that help implement best practices in container security and comply with industry standards.
Use scenarios
Benefits
PT Container Security policies can be flexibly configured to include various types of checks such as:
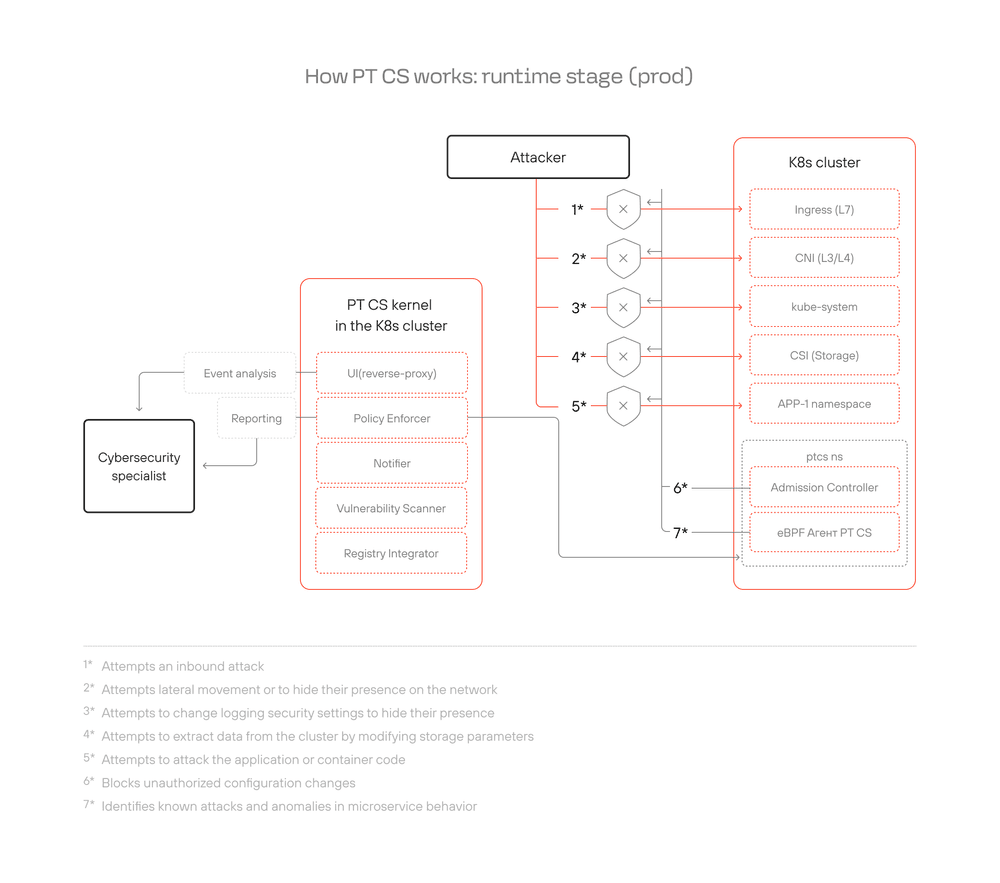
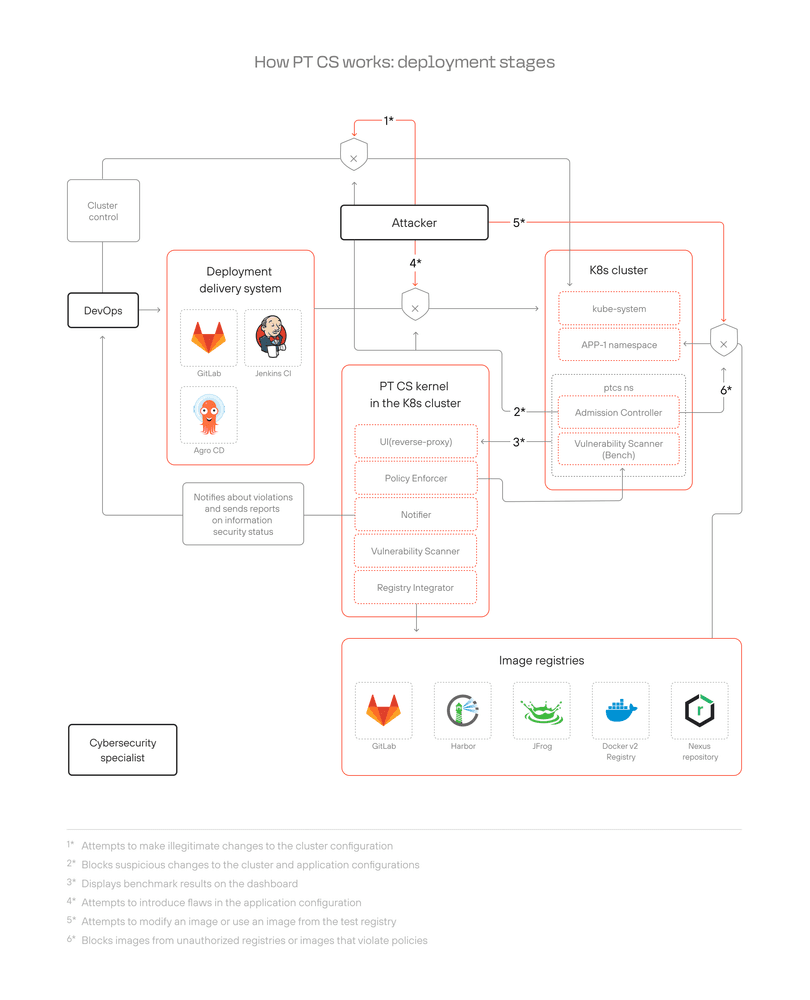
- Admission controlling. A process that validates requests to the Kubernetes API server before they're processed. It allows administrators to control access to the cluster and manage it before applications start running on nodes. Administrators can use admission controllers to define cluster access rules, for example, check for required metadata or certificates, restrict access by IP address, and prevent the creation of objects with unspecified parameters.
- Runtime security. This ensures the active protection of your containers while they're running. The idea is to detect and prevent malicious activity in containers. It's based on Extended Berkeley Packet Filter (eBPF) technology, which allows you to run program code in an isolated virtual machine inside the Linux kernel.
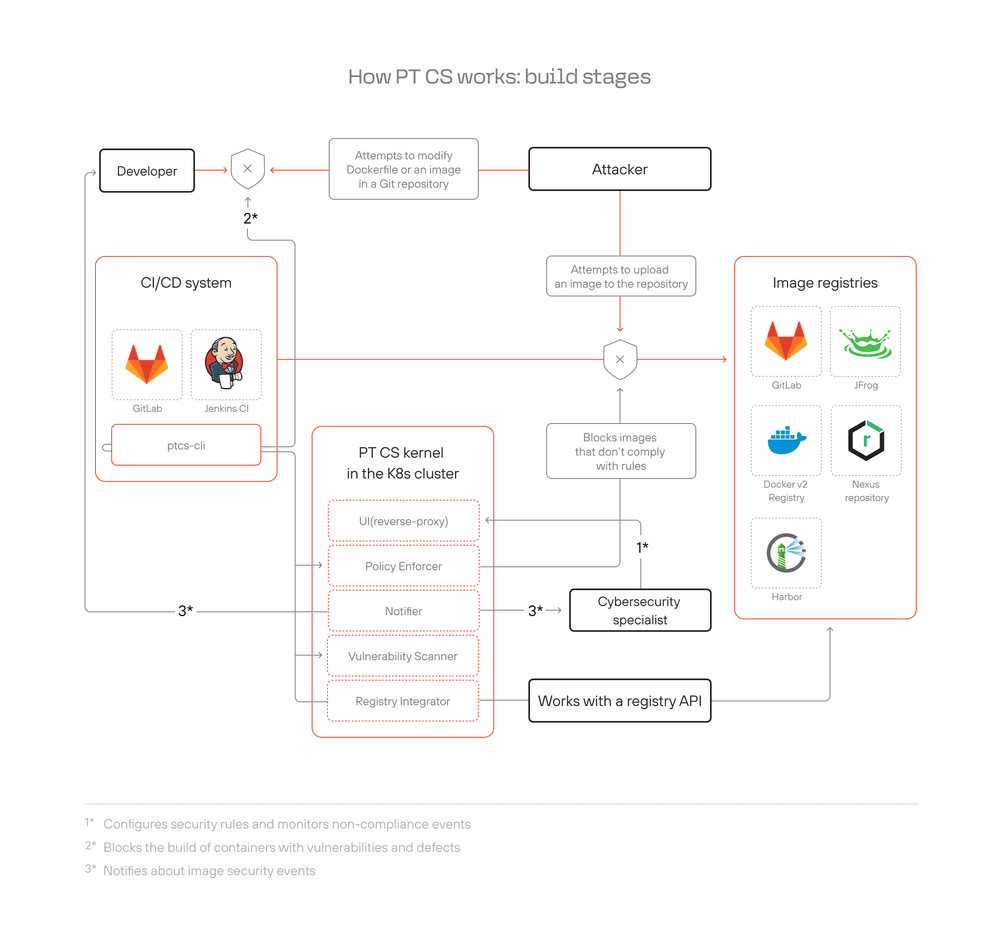
- Image and configuration checks.
Threats addressed by PT Container Security
Automated vulnerability management to address vulnerabilities and flaws in image and container configurations during the build, deployment, and production stages.
Automated security management for Kubernetes cluster configurations.
Automated security incident monitoring and response in container runtime
How to measure efficiency
If you're still undecided on whether to invest in securing your containerized environment, consider the following advantages:
Reduced time to patch.
- Fewer bug reports and vulnerabilities (save on technical support resources).
- Fewer vulnerabilities in the production runtime environment to minimize the risks related to delayed fixes of infrastructure bugs.
- Minimization of unsuccessful project builds during continuous integration
- Fewer errors related to vulnerability or flaw prioritization
Extra materials
Associated products
Thinking about the best way to protect your company?
Contact us.
During the consultation we'll propose a solution precisely tailored to your organization.